AI Security/ISO 42001 Readiness
ISO/IEC 42001 Readiness

ISO 42001 readiness & certification support, auditor brought in for you

Get your AI management system audit-ready: gap assessment, AI risk and impact assessments, policies and technically tested controls. Then compliance as a service through certification, with the auditor brought in for you.

  • Gap analysis against ISO/IEC 42001:2023
  • AI risk assessments and AI system impact assessments
  • AI controls backed by technical test evidence
  • We bring the auditor; an independent certification body certifies
The credentials behind every engagement
CREST-accredited for penetration testingISO/IEC 27001 certifiedSOC 2 Type 2 attested
2026 CyberSecurity Breakthrough Awards winnerG2 High Performer, Fall 2026
Penetration Testing Solution of the Year2026 CyberSecurity Breakthrough Awards
Trusted by Fortune 100, financial services, insurance and SaaS security teams
The short answer

What is ISO 42001 certification?

ISO 42001 certification is independent confirmation that an organization’s Artificial Intelligence Management System (AIMS) meets ISO/IEC 42001:2023. It shows customers and regulators that AI policy, roles, risk and impact assessments and controls are defined, operating and continually improved.

Certification is granted by an independent certification body after a two-stage audit: Stage 1 reviews your documentation and readiness, Stage 2 checks that the management system operates in practice. ioSENTRIX prepares you for both, tests the AI controls technically and brings in the auditor.

ISO 42001 readiness fits when

  • Enterprise customers are asking how you govern AI
  • You already hold ISO/IEC 27001 and want to extend it to AI
  • You build AI into products sold to regulated industries
  • You need a structured AI governance program, certified or not
Your path to certification

One partner from first gap to certification audit.

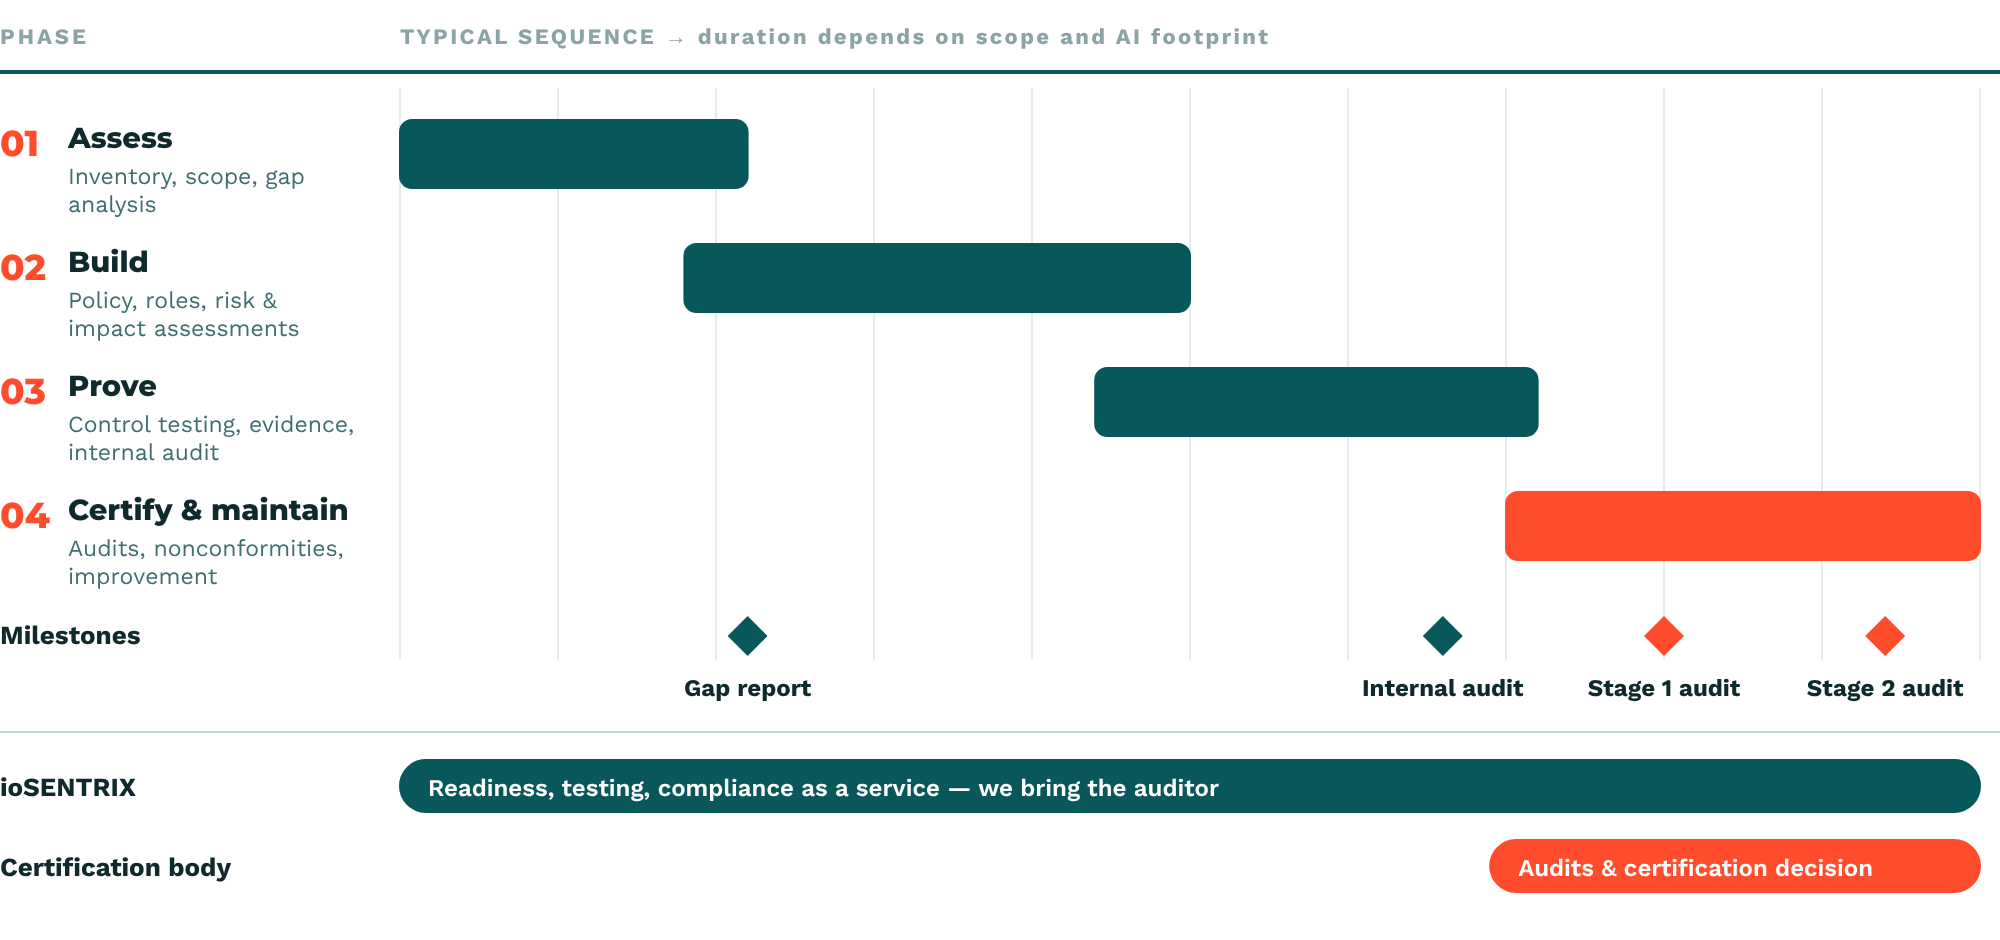
ISO 42001 readiness is a sequence, not a document pack. Phases overlap, and the certification audit is run by an independent certification body.

Exhibit 1
ISO 42001 readiness roadmap, from gap assessment to Stage 2 audit
ioSENTRIX
Swipe sideways to see the full exhibit →
Gantt-style roadmap with four overlapping phases: assess, build, prove, certify and maintain. Milestones: gap report, internal audit, Stage 1 audit and Stage 2 audit. Lanes show ioSENTRIX supporting throughout and the independent certification body running the audits and making the certification decision.
Source: ISO/IEC 42001:2023; ISO/IEC 17021-1 two-stage certification audit model; ioSENTRIX delivery approach. ioSENTRIX is not a certification body.
Reuse what you have

Already ISO 27001 certified? Much of the management system structure carries over to ISO 42001.

Evidence beats documents

We test key AI controls technically, so the evidence an auditor asks for already exists.

No auditor search

We bring the auditor for your certification audit, and stay on for nonconformities and improvement.

What we deliver

How we get you ready for ISO 42001

Four phases, from the first gap assessment to audit day and beyond.

Phase 1

Gap assessment

Where your AI management practices stand against the standard today.

  • AI system inventory
  • Scope & context definition
  • Gap analysis vs ISO/IEC 42001
  • Prioritized remediation plan
Phase 2

AI risk & impact

The risk work at the center of an AI management system.

  • AI risk assessment
  • AI system impact assessment
  • Risk treatment plans
  • Supplier & third-party AI risk
Phase 3

Policies, controls & evidence

Documented processes, and proof that they operate.

  • AI policy & objectives
  • Roles & responsibilities
  • Technical testing of AI controls
  • Audit-ready evidence
Phase 4

Compliance as a service

Ongoing support through certification and beyond.

  • Internal audit support
  • We bring the auditor
  • Nonconformity remediation
  • Continual improvement
Methodology

How we get you ready: example work items

A sample of the work in a typical ISO 42001 readiness engagement.

Clause 4

Scope and AI system inventory

We define the AIMS scope and list the AI systems, their purpose and who is affected by them.

Clause 6

AI risk assessment

We assess AI risks to the organization and set treatment plans with owners.

Clause 6

AI system impact assessment

We assess the potential consequences of each AI system for individuals, groups and society.

Clause 6

Statement of Applicability

We select Annex A controls, justify inclusions and exclusions, and record their status.

Annex A

Technical control testing

We test key AI controls, such as data access and model monitoring, so the evidence is real.

Clause 9

Internal audit and management review

We support the internal audit and management review an auditor expects to see before certification.

Sample gap

What a gap looks like in our report

An illustrative example in our report format. Not client data.

Gap 01 · IllustrativeMajor gap

Impact assessments missing for two customer-facing AI systems

ISO/IEC 42001:2023 · Clauses 6.1.4 and 8.4 AI system impact assessment

What we found

The organization had an AI risk register, but no documented impact assessment for its customer support chatbot or its credit pre-screening model. Neither assessed the consequences for the individuals affected.

Impact

Likely nonconformity at the certification audit, and no evidence for customers who ask how affected individuals are protected.

How to fix it

Run and document impact assessments for both systems, link the results to risk treatment, and set a trigger to repeat them when a system changes.

What you get

What you get from ISO 42001 readiness

Everything an auditor will ask for, and someone to stand next to you on audit day.

1

Gap report and roadmap

Where you stand against ISO/IEC 42001 today and a prioritized plan to close each gap.

2

AIMS documentation and evidence

AI policy, objectives, roles, risk and impact assessments, Statement of Applicability and tested control evidence.

3

Certification support

We bring in the auditor, support you through the audit and help remediate any nonconformities.

Verified reviews

What security leaders say about working with us

★★★★★
“Unlike other providers, Omair and his team truly dive deep into our infrastructure, delivering findings that go well beyond the surface level. Communication is direct and seamless.”
Jesus B.
Cybersecurity Manager, Banking
Verified G2 review ↗
★★★★★
“We were impressed with ioSENTRIX’s ability to independently validate the security of our customer-facing product.”
Zeehasham R.
Data Scientist, Security Operations · CNA
Verified Clutch review ↗
★★★★★
“The team at ioSENTRIX is professional and highly skilled at their craft.”
Awwab A.
SVP, Chief Information Security Officer
Verified G2 review ↗
How it works

Your path to ISO 42001 certification

One partner from first assessment to certification audit.

01

Assess

Inventory your AI systems, define the scope and measure the gap against ISO/IEC 42001.

First
02

Build

Put the AI policy, risk and impact assessments, roles and controls in place.

Next
03

Prove

Test key AI controls and collect the evidence an auditor will ask for.

Before audit
04

Certify and maintain

We bring in the auditor for your certification audit, then support continual improvement.

Audit and after
Reply within 1 business day → fixed quote in writing → readiness → certification audit by an independent body
How we compare

Readiness with technical evidence behind it

How ioSENTRIX ISO 42001 support compares with the usual alternatives.

ioSENTRIX
Templates & toolkits
Documentation-only consultancy
Gap assessment
Against your real AI systems
Self-assessed
Yes
Control evidence
Technically tested by offensive testers
None
Documents only
Certification audit
We bring the auditor
You find one
Often you find one
After certification
Compliance as a service
None
Varies
Scope and price

What affects the scope and price of ISO 42001 readiness

Readiness engagements are priced on effort. These are the decisions that move the quote.

What moves the quote

  1. 01How many AI systems and business units are in the AIMS scope
  2. 02Whether you already run ISO/IEC 27001 or another management system
  3. 03How many AI controls are tested technically
  4. 04Your target audit date
  5. 05Whether compliance as a service continues after certification
Read: ISO 42001 explained: the AI management system standard →

What we need from you to start

  • A list of AI systems you build, buy and use
  • Existing ISO/IEC 27001 or other management system documents
  • An executive sponsor and an AIMS owner
  • Your target date for the certification audit
Start my gap assessment
Proof, not promises

AI systems we have already tested

A real engagement, described without the client’s name.

Case study

Fortune 500 financial services: AI/ML threat model across AWS and Azure

We threat-modeled the client’s AI estate — RAG pipelines, LLM orchestration layers and ML inference workflows — using STRIDE, NIST SP 800-30 and the NVIDIA AI Red Team framework.

Read the case study →
30+
AI components reviewed across AWS and Azure
13
threats identified and mapped
5
high-severity threats in RAG, orchestration and inference
Clients: Fortune 100, financial services, insurance and SaaS. Engagements: 2 weeks to 4 months, quoted on effort.
RAG systemsCustom LLM pipelines & trainingChatbotsOrganization-wide AI enablementAI features in SaaS productsMCP testing
Track record

Numbers you can check

Ratings you can verify on G2 and Clutch.

G2
4.9 / 5
on G2 from 12 verified reviews
Clutch
5.0 / 5
on Clutch, Premier Verified
2017
founded; CREST-accredited, ISO 27001 certified, SOC 2 Type 2 attested
Who you work with

Who does the testing

Offensive security engineers do the hands-on testing and write up the findings, so the person who found an issue explains it to your team.

Certified testers

Each tester holds one or more of OSCP, OSWE, OSCE, CISSP, CISA or AWS security certifications.

Accredited firm

ioSENTRIX is CREST-accredited for penetration testing, ISO/IEC 27001 certified and SOC 2 Type 2 attested.

Since 2017

Founded in 2017, with offensive security work for Fortune 100, financial services, insurance and SaaS companies.

Customers asking how you govern AI?

A senior engineer replies within 1 business day · no sales pitch

Start my gap assessment
Standards

Frameworks we test and map to

◆ISO/IEC 42001:2023◆ISO/IEC 27001◆NIST AI RMF◆OWASP Top 10 for LLM Applications◆MITRE ATLAS
FAQ

Frequently asked questions

What is ISO 42001?

ISO/IEC 42001:2023 is an international standard for establishing, implementing, maintaining and continually improving an Artificial Intelligence Management System (AIMS). It covers how an organization sets AI policy, assigns responsibilities, assesses AI risks and impacts, and operates controls. Read our ISO 42001 explainer.

Does ioSENTRIX issue the ISO 42001 certificate?

No. Certification is granted by an independent certification body after an audit. ioSENTRIX prepares you for that audit, supports you through it with compliance as a service, and brings in the auditor so you do not have to find one yourself.

How does ISO 42001 relate to ISO 27001?

Both are management system standards. ISO 27001 covers information security; ISO 42001 covers the responsible management of AI. Organizations that already run an ISO 27001 program can often reuse much of its structure.

Does ISO 42001 certification make us compliant with the EU AI Act?

Not automatically. ISO 42001 is a voluntary standard, while the EU AI Act is a regulation with legal obligations that depend on your role and AI systems. An AI management system can support your compliance work, but it does not replace it.

How long does it take, and how is it priced?

It depends on how many AI systems are in scope and how mature your management system already is. Each engagement is a fixed quote based on effort, bought with PTaaS credits or a subscription.

Who can certify an organization to ISO 42001?

Only a certification body can issue ISO/IEC 42001 certification, and buyers usually look for one accredited for ISO 42001. ISO/IEC 42006:2025 sets the requirements for bodies that audit and certify AI management systems. ioSENTRIX is not a certification body; we prepare you and bring the auditor in.

Ready when you are

Get audit-ready for ISO 42001

Tell us about your AI systems and your target date. We will scope the gap assessment and send a fixed quote based on effort.

A senior engineer replies within 1 business day · Fixed quote in writing before work starts · Your details are never shared