About us · Since 2017

About ioSENTRIX

ioSENTRIX is a CREST-accredited offensive security firm, founded in 2017 and based in Herndon, Virginia. Our own testers find the weaknesses attackers would use, prove them, and stay with you until they are fixed and your auditor accepts the report.

Trusted by security teams at
Decorative
Decorative
Decorative
Decorative
Decorative
Decorative
Decorative
Decorative
Decorative
Decorative
Decorative
Decorative
Decorative
Decorative
Decorative
Decorative
Decorative
Decorative
Who we are

An offensive security firm built on proof, not promises

ioSENTRIX is a cybersecurity firm that tests software, networks, cloud and AI systems the way real attackers would. We run penetration testing, penetration testing as a service (PTaaS), application security, red teaming, AI security testing, continuous threat exposure management (CTEM) and vCISO services.

Every engagement is carried out by ioSENTRIX's own testers, never a crowd or freelancers. Every fix is retested for free, the price is fixed unless the scope changes, and we work with your auditor until the report is accepted.

We work with Fortune 100 retailers, Fortune 500 insurers, financial services firms, SaaS companies and security software vendors, and with startups preparing for their first SOC 2 or ISO 27001 audit.

Credentials

Independently accredited and audited

What we hold as a company, and what our testers hold as individuals.

CREST accredited for penetration testing

CREST-accredited

ioSENTRIX is accredited by CREST, the international body for technical security services, for penetration testing. The accreditation covers our methodology, quality and governance.

ISO/IEC 27001 certified

ISO/IEC 27001 certified

Our information security management system is certified to ISO/IEC 27001 by an accredited certification body.

SOC 2 Type 2 attested

SOC 2 Type 2 attested

An independent auditor has examined our controls over time. You can request the report from our Trust Center.

Certifications held across our testing team
  • OSCP
  • OSWE
  • OSCE
  • CEH
  • ECSA
  • CPTE
  • CISSP
  • CISA
  • CAP
  • CompTIA Security+
  • AWS Certified Security – Specialty
  • AWS Solutions Architect – Associate

Each consultant holds one or more of these. CREST accreditation is held by ioSENTRIX as a company.

Recognition

Awards and independent ratings

What judges and verified clients say, with links to the source.

“There are countless security vendors out there in the market. We picked ioSENTRIX for their expertise across various domains. They have pen-tested our IoT devices, micro-services, web services, and other deployments.”
Director IT Security, leading advisory firm
“When it comes to full stack penetration testing, ioSENTRIX has always been our first choice. Most vendors offer only automated testing whereas ioSENTRIX supplements automation along with manual testing to provide in-depth coverage.”
Founder & CEO, enterprise software company
“ioSENTRIX has always provided unparalleled insight, advice, and knowledge about security vulnerabilities across our environment.”
CIO, unicorn startup
Leadership

Meet our leadership

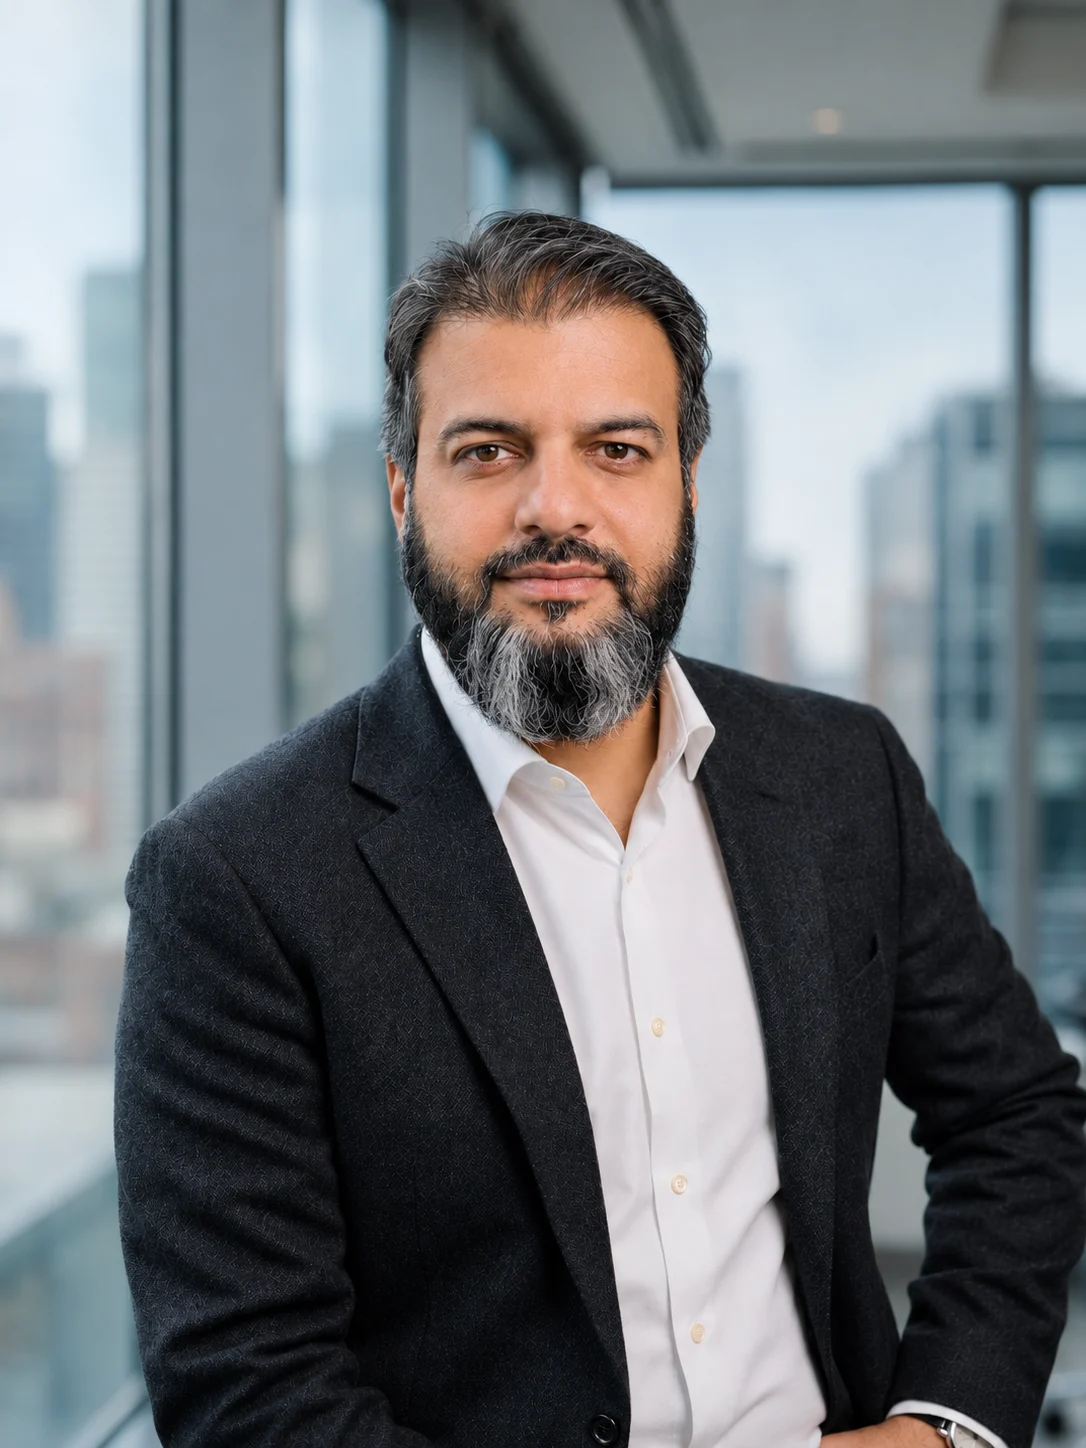
Omair Manzoor

Founder, CEO & Chief Hacker

Omair founded ioSENTRIX in 2017 and leads it as CEO and Chief Hacker. He remains hands-on in client delivery.

He has more than 20 years in offensive security. Exploits he developed are included in the Metasploit Framework, Immunity Canvas and Core Impact, the exploitation frameworks penetration testers rely on.

Before ioSENTRIX he worked on product security for the Alexa and Fire TV product lines at Amazon Lab126, and on penetration testing, secure code review and architectural risk analysis at Cigital (now part of Synopsys) for financial services, gaming and technology clients. He has tested systems from subway train control to banking platforms, in code bases from a few thousand to tens of millions of lines.

  • Published researcher with responsible disclosures to vendors including Microsoft
  • Keynote speaker; has presented at events hosted by the Department of Defense, CISA and BSides
  • BSides CFP Board Member and Reviewer
  • Technical reviewer of Computer Security (2nd edition) by William Stallings
  • Quoted as a security expert in Forbes and TechRound

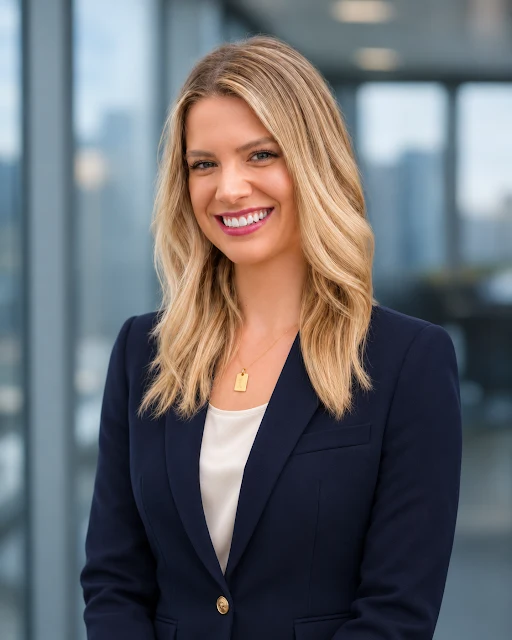
Becky Mickelsen

Senior Vice President, Sales & Revenue

Becky leads revenue strategy, business development, and strategic client relationships at ioSENTRIX, driving growth through new market opportunities, strategic partnerships, and long-term client engagement.

With more than a decade of experience spanning sales leadership, business development, account management, and client services, she brings a strong understanding of the full client lifecycle—from identifying opportunities and developing relationships to delivering lasting business value.

Her approach is grounded in trust, accountability, and a commitment to understanding each client's unique challenges. At ioSENTRIX, she focuses on connecting organizations with cybersecurity solutions that meet their evolving needs while building partnerships that support sustainable growth.

  • Leads revenue strategy, sales, and business development
  • Drives strategic client relationships, retention, and account growth
  • Develops channel partnerships and new market opportunities
Our story

Why ioSENTRIX exists

Omair founded ioSENTRIX in 2017 after years on both sides of security testing: delivering it as a consultant, and buying it while leading product security at Amazon. Too often he saw organizations given a false sense of security: automated scans presented as penetration tests, narrow scopes, and jargon-heavy reports with no business context.

ioSENTRIX was built to do the opposite. Manual testing by experienced people, supported by automation rather than replaced by it. Reports that explain business risk. Free retesting, so a finding is closed only when the fix is proven. That is still how we work.

01

Proof, not promises

We show you what an attacker could do, with steps to reproduce it. No inflated scores and no padded reports.

02

Your success is our success

Retests are free and we stay with you until your auditor accepts the report, because a finding only matters once it is fixed.

03

The whole picture

Code, cloud, network, people and AI are tested together, because attackers do not respect scoping boundaries.

How we work

Six commitments on every engagement

Our own testers

Every test is run by ioSENTRIX staff. No crowd, no freelancers.

Free retests

Every fix is retested at no extra cost, so you have proof it holds.

Fixed price

The quoted price only changes if the scope does.

Audit support

We work with your SOC 2, ISO 27001, PCI DSS or HIPAA auditor until the report is accepted.

Fast first reply

We reply to new inquiries in under an hour.

Published methods

We test against published methods such as the OWASP testing guides, MITRE ATT&CK and MITRE ATLAS, and map findings to your compliance requirements.

As featured in

ioSENTRIX in the news

Coverage and expert commentary from our team.

ForbesCSO OnlineTechopediaKTBS 3Local 3 NewsCRM MagazineSmarterMSPTechRoundMoonlockPaubox
See all coverage in the Newsroom →
FAQ

Frequently asked questions

Short answers about ioSENTRIX.

Ask us something else

What is ioSENTRIX?

ioSENTRIX is a CREST-accredited offensive security firm founded in 2017 and based in Herndon, Virginia. It provides penetration testing, PTaaS, application security, red teaming, AI security testing, CTEM and vCISO services, carried out by its own testers.

Who founded ioSENTRIX?

Omair Manzoor founded ioSENTRIX in 2017 and is its CEO and Chief Hacker. He has more than 20 years in offensive security, and exploits he developed are included in the Metasploit Framework, Immunity Canvas and Core Impact. Before ioSENTRIX he worked on product security at Amazon Lab126 and on security consulting at Cigital (now part of Synopsys).

Is ioSENTRIX CREST accredited?

Yes. ioSENTRIX is CREST-accredited for penetration testing. It is also ISO/IEC 27001 certified and SOC 2 Type 2 attested, and the SOC 2 report can be requested from the ioSENTRIX Trust Center.

What awards has ioSENTRIX won?

ioSENTRIX was named Penetration Testing Solution of the Year in the 2026 CyberSecurity Breakthrough Awards. It is a G2 High Performer for Fall 2026, rated 4.9 out of 5 from 12 reviews on G2, and rated 5.0 out of 5 on Clutch.
Who carries out ioSENTRIX tests?

ioSENTRIX's own testers carry out every engagement; it does not use a crowd or freelancers. Its testers hold certifications including OSCP, OSWE, OSCE, CISSP and AWS Certified Security - Specialty.

Where is ioSENTRIX located?

ioSENTRIX is headquartered at 13800 Coppermine Rd, Suite 190, Herndon, Virginia 20171, and works with clients across the United States and internationally.

Talk to ioSENTRIX

Tell us what you need tested. We reply in under an hour with next steps, and the price we quote stays fixed unless the scope changes.

Client Testimonial

testimonial
There are countless security vendors out there in the market. We picked ioSENTRIX for their expertise across various domains. They have pen-tested our IoT devices, micro-services, web services, and other deployments. We are immensely satisfied with their results and they have made a positive and lasting impression.
Director IT Security,  Leading Advisory Firm
testimonial
When it comes to full stack penetration testing, ioSENTRIX has always been our first choice. Most vendors offer only automated testing whereas ioSENTRIX supplements automation along with manual testing to provide in-depth coverage. We completely trust their remediation strategies.
Founder & CEO,  Enterprise Software Development Company
testimonial
ioSENTRIX has always provided unparalleled insight advice, and knowledge about security vulnerabilities across our environment. We are extremely pleased with their efforts and advice.
CIO,  Unicorn Startup
Decorative
Decorative

As Featured in