August 27, 2026
AI Integrity: Why Proving an Autonomous Action Is Real Is the Next Security Problem
AI Integrity: Why Proving an Autonomous Action Is Real Is the Next Security Problem
Omair


Omair Manzoor is the Founder, CEO, and Chief Hacker of ioSENTRIX, a CREST-accredited cybersecurity firm. With 14+ years in offensive security, he has led penetration tests for Fortune 500 companies including engagements for Amazon, Bank of America, VISA, and the London Underground. His exploits are part of the Metasploit Framework and Immunity Canvas. Omair is a published researcher, conference keynote speaker (DOD, CISA, BSides), and technical reviewer for academic security textbooks.
AI-driven applications are transforming industries, enabling smarter automation, enhanced decision-making, and personalized experiences. From chatbots and recommendation engines to fraud detection systems, AI is now an integral part of software development.
However, with these advancements come unique security challenges that traditional application security (AppSec) practices may not fully address.
In this blog, we’ll explore the best practices for securing AI-driven applications and how ioSENTRIX leverages advanced techniques to protect your AI-powered systems.
AI-driven applications introduce a distinct set of security risks, including:
These risks require a tailored approach to application security that considers the entire AI lifecycle—from data collection and model training to deployment and maintenance.
Data integrity is foundational to AI security. Ensure that data used for training and inference is protected against tampering and unauthorized access.
Best Practices:
APIs are often the gateway to AI functionality, making them a prime target for attackers.
Best Practices:
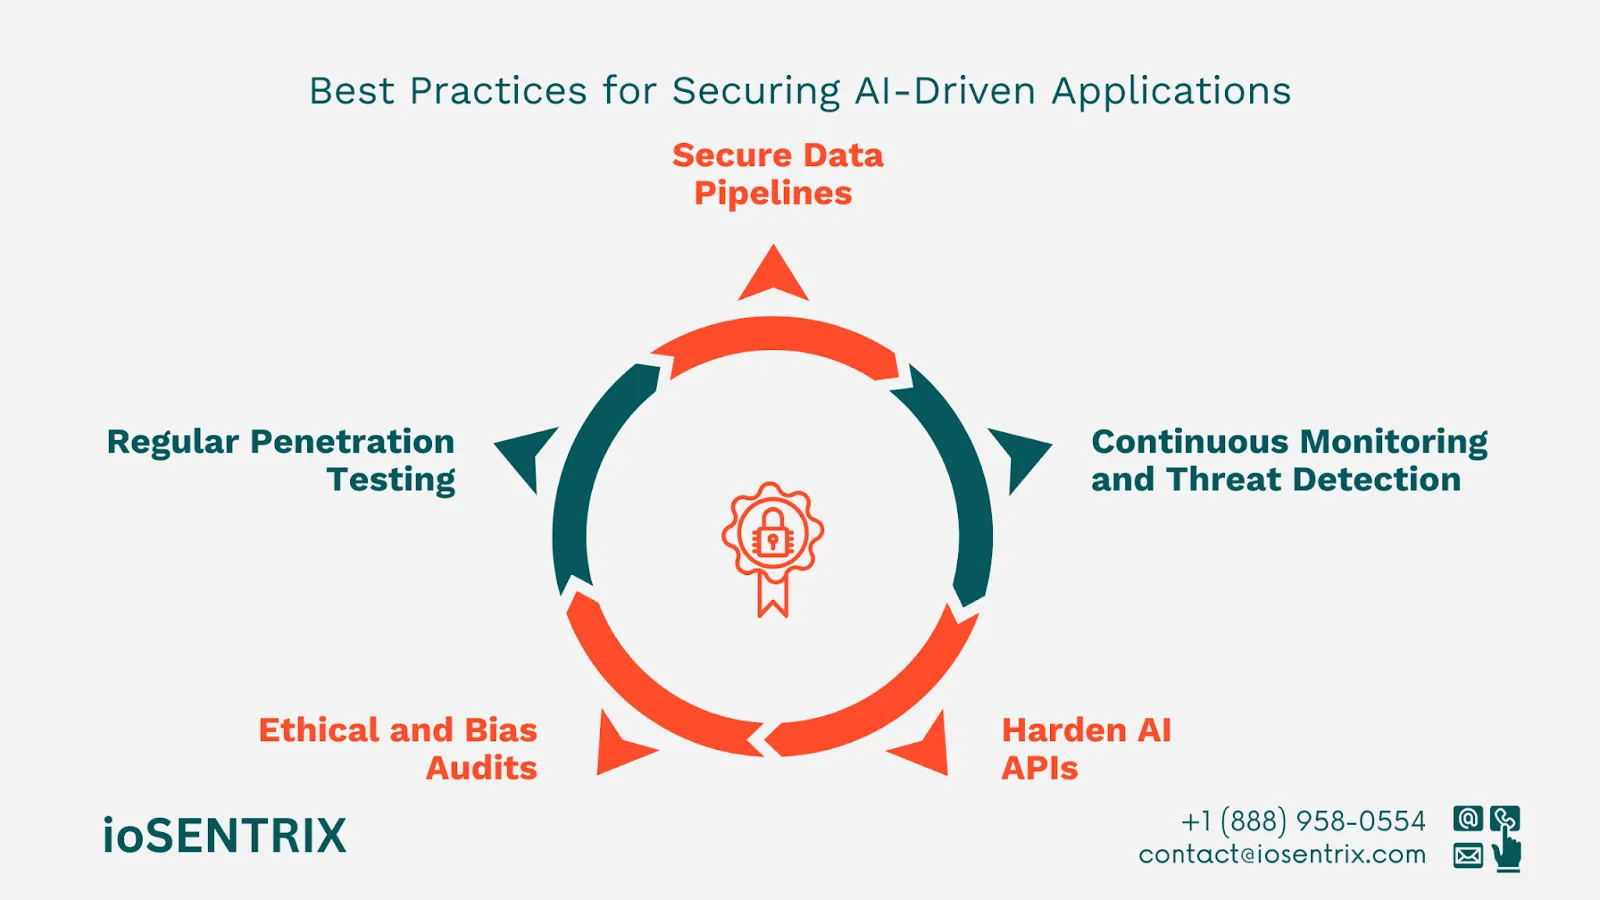
Traditional penetration testing must evolve to address AI-specific vulnerabilities. ioSENTRIX’s AI-aware pentesting identifies risks unique to AI-driven applications.
Best Practices:
AI applications require real-time monitoring to detect emerging threats and anomalies.
Best Practices:
Bias in AI can lead to harmful outcomes, damaging brand reputation and violating regulations.
Best Practices:
At ioSENTRIX, we specialize in securing AI-powered systems through:
A leading e-commerce platform leveraging AI for personalized recommendations.
Ensuring the security and integrity of their recommendation engine while maintaining high performance.
As AI continues to drive innovation, securing these applications becomes critical. ioSENTRIX offers a comprehensive suite of services to address the unique security challenges posed by AI-driven applications, ensuring your systems remain secure, compliant, and trustworthy.
Secure your AI applications today! Contact ioSENTRIX for a consultation.