September 24, 2026
The Reflected XSS Methodology: 11 Labs Behind $5,000+ in Bounties and 80+ Pentests
The Reflected XSS Methodology: 11 Labs Behind $5,000+ in Bounties and 80+ Pentests
Salman Khan


Fiza Nadeem is an SEO content writer at ioSENTRIX with 2.5+ years of experience in content writing, copywriting, and SEO.
Data encryption solutions are the products, services and controls that turn readable data into ciphertext and manage the keys that turn it back. They cover data at rest on disks and in databases, data in transit across networks, and, increasingly, data in use inside a processor. Most organizations already run several of them, often without a list of which ones, where the keys live, or whether any of it has been tested.
This guide explains the types of data encryption solutions with examples, how database encryption solutions and enterprise key management work, which compliance rules drive the decision, and why encryption that exists on paper so often fails under test. ioSENTRIX does not sell encryption products. We test whether the encryption you already have holds.
Data encryption solutions are software, hardware or managed services that apply cryptographic algorithms to protect data and that manage the keys, policies and access controls around that protection. The definition matters because the algorithm is rarely the weak point. The solution is the whole system: where encryption is applied, who holds the keys, how keys rotate, and what happens when a key or a backup leaves the building.
An encryption solution should answer four questions. What data is encrypted? Where in the stack does it happen? Who can obtain the key? What evidence shows it works? If a vendor or an internal team cannot answer all four, you have a feature, not a solution. Our glossary entry on encryption covers the basics.
Encryption uses an algorithm and a key to convert plaintext into ciphertext, and the correct key to reverse it. Symmetric algorithms use one key for both directions and are fast, so they protect bulk data. Asymmetric algorithms use a public and private key pair and are slower, so they exchange symmetric keys and sign data.
The workhorse symmetric algorithm is AES, specified by NIST in FIPS 197 with 128-, 192- and 256-bit keys. NIST withdrew the older DES standard in 2005, and SP 800-131A Rev. 2 disallows three-key Triple DES for new encryption after 2023, so both are legacy when a scan turns them up. On the asymmetric side, RSA and elliptic-curve cryptography (ECC) carry most key exchange and signature work; ECC gives comparable security with shorter keys, which is why it dominates on constrained devices.
Quantum computing is why algorithm choice is back on the agenda: NIST published its first post-quantum standards, FIPS 203, 204 and 205, in August 2024, and long-lived data protected only by RSA or ECC key exchange has a shelf life. See our glossary on post-quantum cryptography.
Data encryption solutions fall into three groups based on the state of the data: at rest, in transit and in use. Each solves a different problem and fails in its own way, and most organizations need all three.
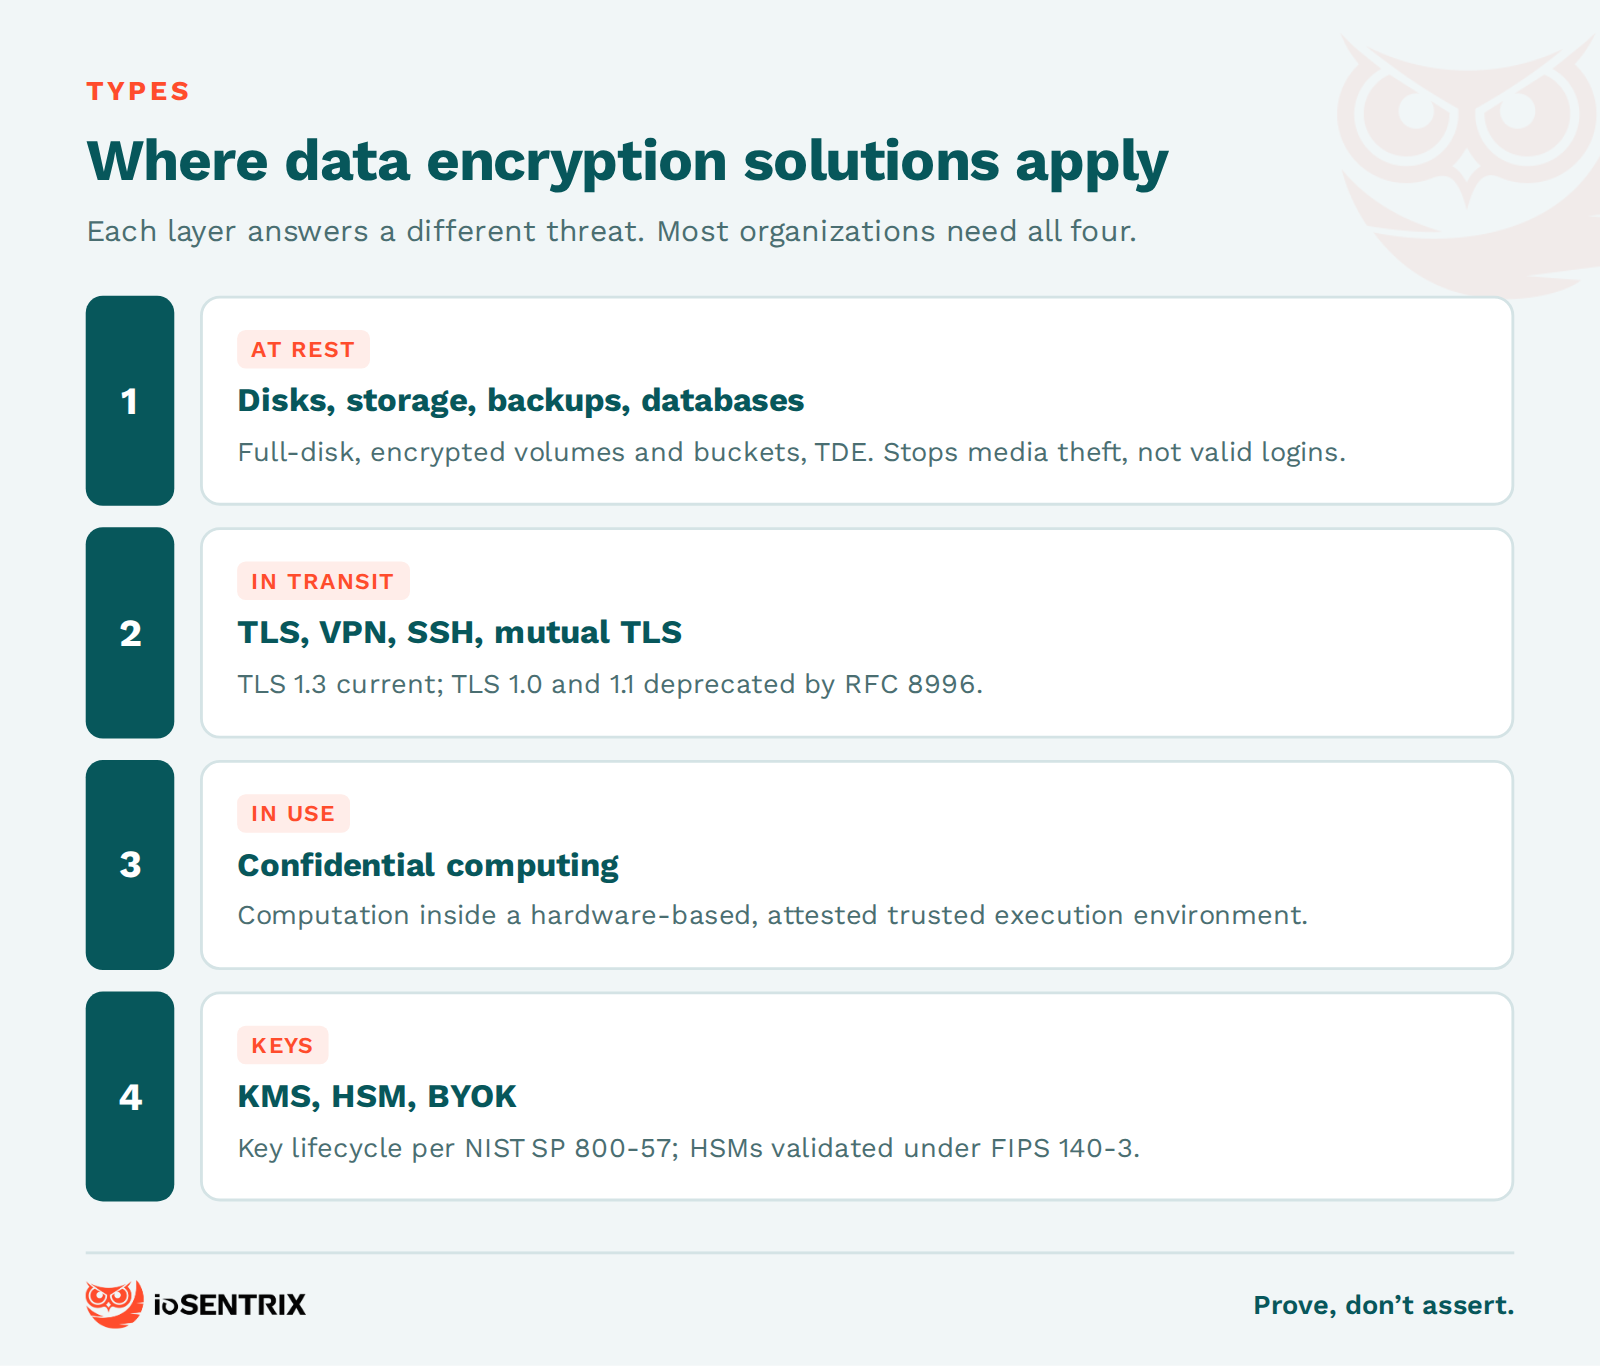
Data at rest encryption solutions protect stored data on disks, file systems, object storage, backups and databases. Examples include full-disk encryption on laptops and servers, encrypted cloud volumes and storage buckets, encrypted backup targets, and database-level encryption, covered below. They protect against lost or stolen media and against anyone who reads raw storage without going through the system's access controls. They do not protect against an attacker who logs in with valid credentials, because the system decrypts the data for that user as it would for anyone else.
Data in transit encryption solutions protect data as it moves between users, services and data centers. The standard example is TLS, which secures HTTPS, most APIs and many database connections. The current version is TLS 1.3, and the IETF formally deprecated TLS 1.0 and 1.1 in RFC 8996. Other examples include VPN and IPsec tunnels, SSH for administrative access, and mutual TLS between microservices. The recurring failure is not the protocol but the configuration: legacy versions left on, weak cipher suites accepted, certificates unvalidated, or an internal hop where encryption was assumed and never turned on.
Data in use encryption solutions protect data while it is being processed, which is where at-rest and in-transit encryption both stop. The Confidential Computing Consortium defines confidential computing as the protection of data in use by performing computation in a hardware-based, attested trusted execution environment; cloud providers now sell confidential virtual machines built on that model. Application-level encryption, covered below, is the more common way to shrink the window in which plaintext exists.
Database encryption solutions protect the data inside a database engine at one of three levels: the whole data file, individual columns or fields, or the application layer above the database. The right level depends on who you are defending against. The trade-off is the same in every product: the more transparent the encryption is to applications, the less it protects against anyone with database access.
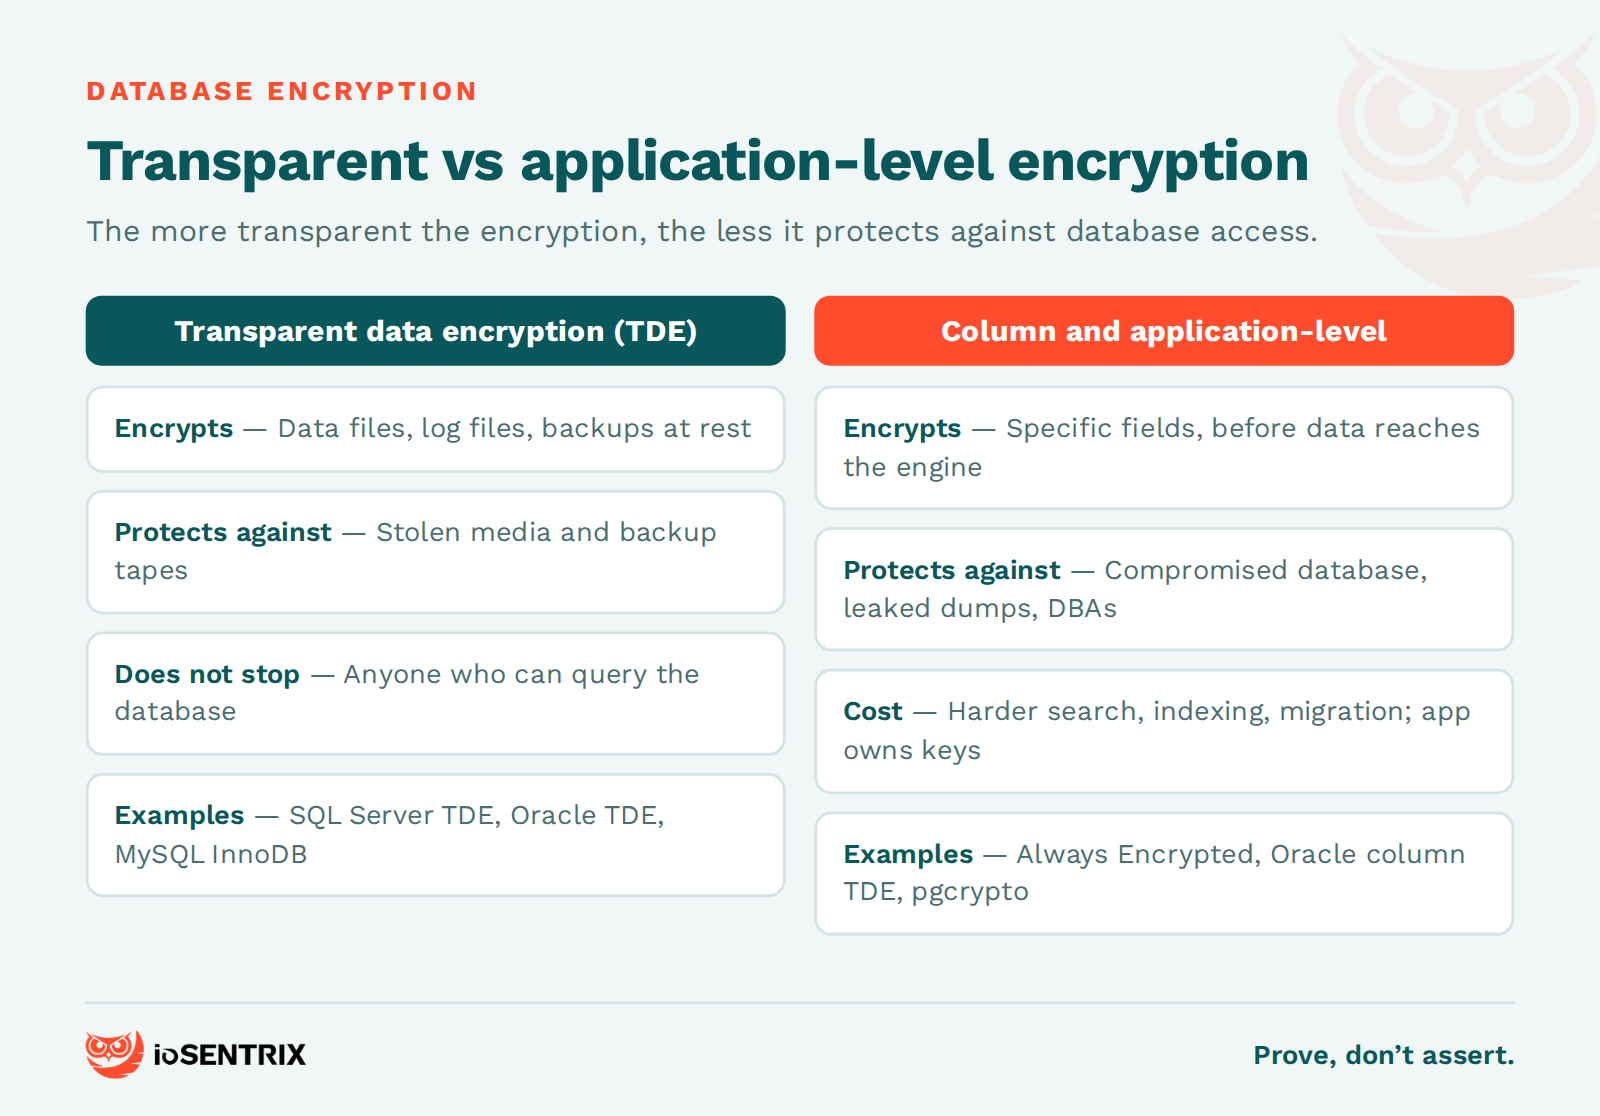
Transparent data encryption encrypts the database's data files, log files and backups at rest with no change to the application. Microsoft SQL Server, Oracle Database and MySQL's InnoDB engine all ship a version of it. Microsoft's documentation is clear about what TDE is for: a party who steals physical media or backup tapes cannot restore and browse the data. It is equally clear about what it is not for: anyone who can query the database sees plaintext, and TDE provides no protection across communication channels. TDE answers "what if someone steals a backup," not "what if someone gets a database login."
Column-level encryption encrypts specific fields, such as card numbers or national identifiers, with keys held outside the database. Examples include Always Encrypted in SQL Server, which encrypts client-side so the database engine never holds the key and database administrators cannot read the plaintext; Oracle TDE column encryption; and the pgcrypto module in PostgreSQL, which gives developers per-column encryption functions. Application-level encryption moves the same idea up a layer: the application encrypts before writing and decrypts after reading, so a compromised database or a leaked dump yields ciphertext. The cost is real. Encrypted columns are harder to search, index and migrate, and the application now owns key handling, which is where most implementations go wrong.
Tokenization is a related option: it replaces a sensitive value with a stand-in that has no mathematical relationship to the original and keeps the mapping in a separate vault. It is not encryption, but it takes real card numbers out of most systems.
Enterprise data encryption solutions are centralized key management systems, hardware security modules and the policies that connect them to every encrypting application. At small scale, keys live wherever the developer put them. At enterprise scale, key management is the actual product and the algorithms are a detail.
NIST's SP 800-57 Part 1 is the standard reference for the key lifecycle: generation, storage, distribution, rotation, revocation and destruction. A key management system (KMS) automates that lifecycle and enforces who can use which key for what. A hardware security module (HSM) is tamper-resistant hardware that generates and holds keys so they never exist in plaintext outside it; FIPS 140-3 is the NIST standard that validates cryptographic modules, including HSMs. Our glossary defines key management in more depth.
Cloud data encryption solutions are the provider-native key services and the encryption built into cloud storage and databases. AWS KMS, Azure Key Vault and Google Cloud KMS each let you create and control keys, back them with validated HSMs at their higher tiers, and apply them to storage, databases and secrets through the provider's APIs. All three use a hierarchy in which an HSM-protected root key wraps the data keys that do the actual encryption. Bring your own key (BYOK) and external key management let you hold the root key yourself, which matters for regulated workloads and for the question every cloud customer eventually asks: who can decrypt my data without asking me? A cloud penetration test usually finds the harder problem is not the KMS configuration but the IAM roles granted decrypt permission and never reviewed.
Data encryption software is a product you deploy and operate: disk encryption agents, database encryption features, KMS platforms, TLS termination. Data encryption services are the same capabilities run by someone else: managed KMS and HSM offerings in the cloud, managed encryption for SaaS data, or a consultancy that operates the key program. Software gives you control and the full operational burden. Services shift the burden, but not the accountability. Either way, the questions that decide security are the same: who holds the keys, who can be compelled to use them, and what proof exists that the controls work.
The three regulations buyers cite most are PCI DSS, HIPAA and GDPR, and none of them names a product. PCI DSS Requirement 3 covers protecting stored account data and Requirement 4 covers strong cryptography for cardholder data in transit over open, public networks; our guide to PCI DSS 4.0 penetration testing requirements covers the testing side. The HIPAA Security Rule lists encryption of electronic protected health information as an addressable implementation specification at 45 CFR 164.312, meaning a covered entity implements it or documents why an alternative is reasonable; see our guide to HIPAA penetration testing. GDPR Article 32 names encryption of personal data as an example of an appropriate technical measure.
Each framework asks you to encrypt and to demonstrate it. Compliance automation tools collect the configuration evidence. They cannot tell you whether the configuration holds against an attacker, which is what an auditor increasingly wants to know and what a penetration test provides.
Encryption fails in practice because of key handling, configuration and gaps between layers, far more often than because of a broken algorithm. OWASP ranks Cryptographic Failures at A04 in the OWASP Top 10:2025, and the category is about exactly these mistakes: clear-text storage or transmission, legacy algorithms still enabled, default or hard-coded keys, and missing key rotation.
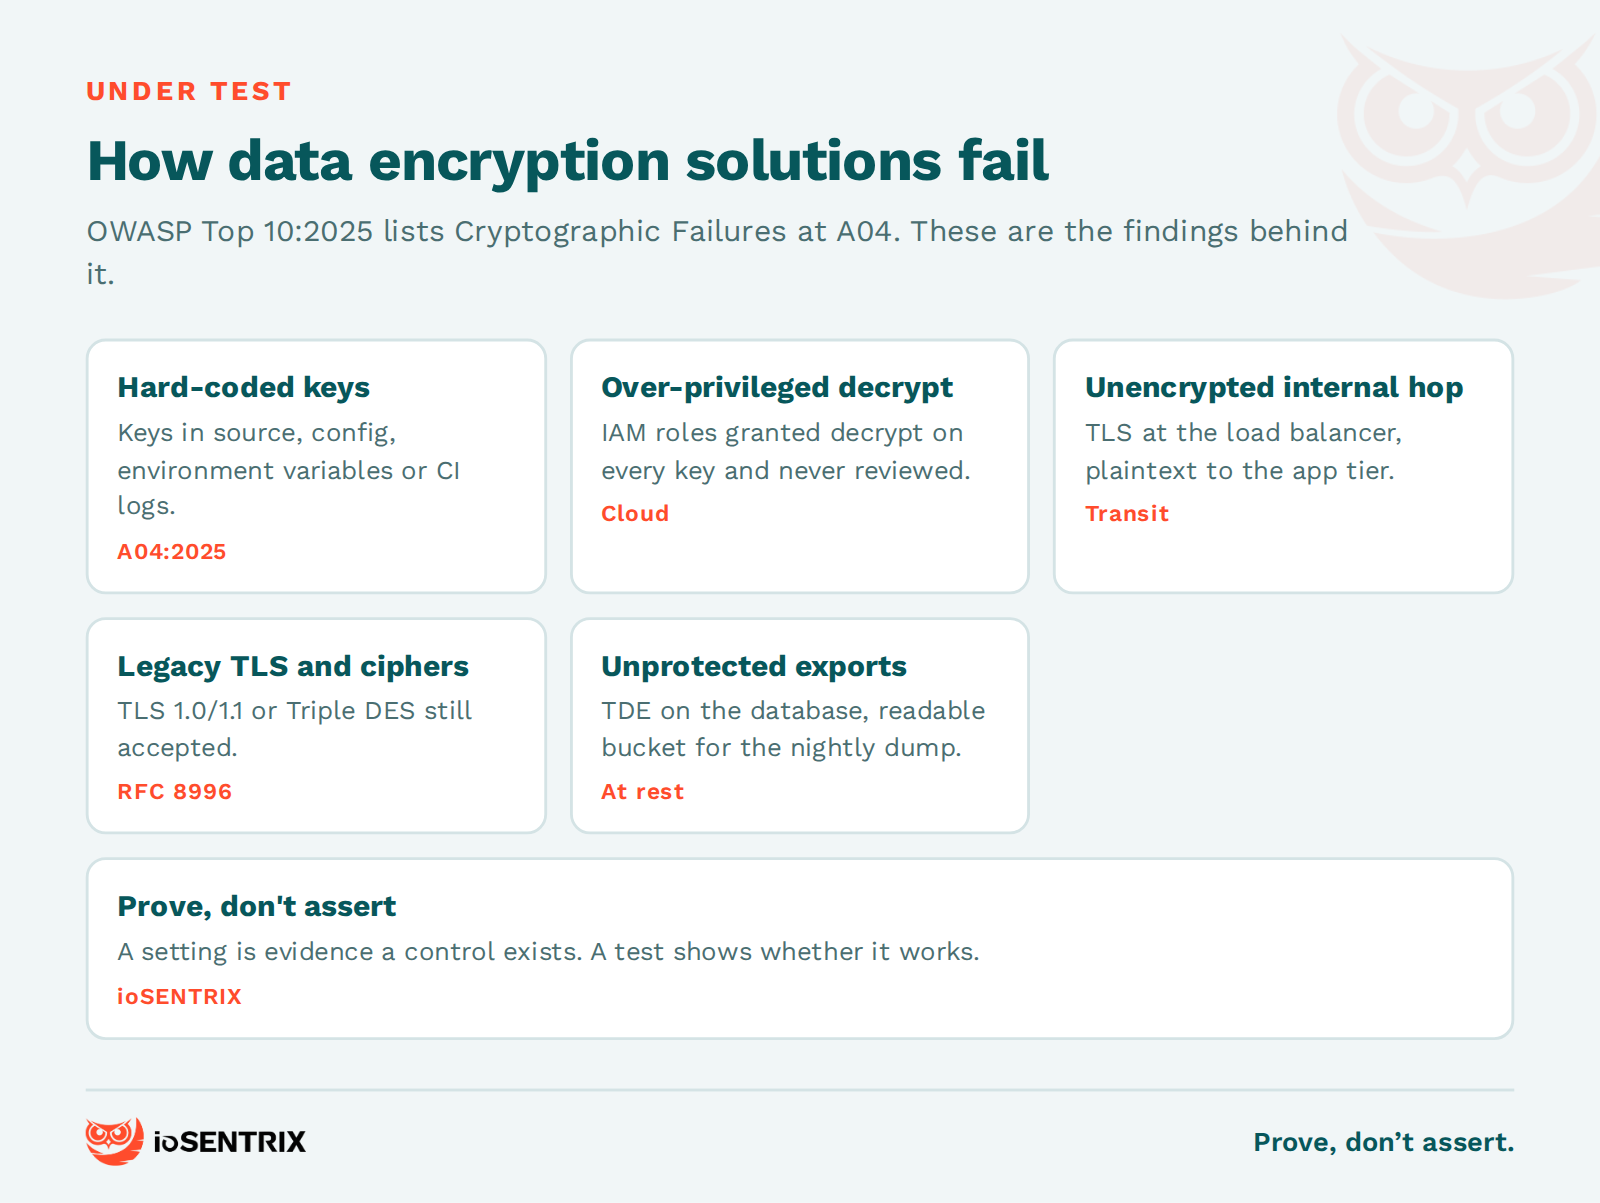
Here is a composite drawn from engagements, not any one client. A SaaS company encrypted its production database with TDE and could show the auditor the setting. The nightly export of that database landed in a storage bucket with encryption enabled and a bucket policy readable by every engineer's role. The application encrypted card tokens with a key held in an environment variable that was also written to CI build logs. TLS was enforced at the load balancer and absent between the balancer and the application tier. Every control existed. Three of the four did nothing against the attacker who mattered.
That is the difference between a control that exists and a control that works, and it is why we test evidence rather than settings. In a web application penetration test we look for keys in source, configuration and logs; in a mobile application penetration test, for local storage and certificate pinning failures; in cloud and network tests, for the internal hop nobody encrypted and the role that can decrypt everything.
Data encryption is the process of converting readable data into an unreadable form using an algorithm and a key, so that only someone holding the correct key can restore it. It protects confidentiality when data is stored, transmitted or, with newer techniques, processed. It does not by itself protect against someone who obtains the key or who is authorized to have the data decrypted for them.
Examples include full-disk encryption on endpoints and servers, TLS for web traffic and APIs, VPN and IPsec tunnels, transparent data encryption in SQL Server, Oracle and MySQL, column-level tools such as Always Encrypted and pgcrypto, cloud key services such as AWS KMS, Azure Key Vault and Google Cloud KMS, on-premises HSMs, and confidential computing for data in use.
There is no single best product. The best enterprise data encryption solution is one whose keys you control through a central KMS, backed by validated HSMs for the root keys, covering data at rest, in transit and, where the risk warrants it, in use, with evidence that the configuration holds under adversarial testing. Choose by threat model and key ownership, not feature list.
Data-at-rest encryption protects stored data on disks, file systems, object storage, databases and backups so the raw storage is unreadable without the key. It defends against lost or stolen media and direct reads of storage. It does not defend against an attacker using valid credentials, which is why it is paired with access control and, for sensitive fields, application-level encryption.
ioSENTRIX is a CREST-accredited penetration testing firm, ISO/IEC 27001 certified and SOC 2 Type 2 attested. We do not sell encryption products. Our penetration testing and application security services test the encryption and key handling you already have: where keys are stored, who can use them, which paths are encrypted end to end, which backups and exports are not, and whether the compliance evidence describes a control that holds against a real attacker. Prove, don't assert.
If you want an independent answer to "who could decrypt our data, and how," talk to us about scoping an assessment.