September 24, 2026
The Reflected XSS Methodology: 11 Labs Behind $5,000+ in Bounties and 80+ Pentests
The Reflected XSS Methodology: 11 Labs Behind $5,000+ in Bounties and 80+ Pentests
Salman Khan


Fiza Nadeem is an SEO content writer at ioSENTRIX with 2.5+ years of experience in content writing, copywriting, and SEO.
Penetration testing companies are not interchangeable, and the differences rarely show up in the proposal. Two firms can quote the same scope and name the same standards while one spends three days exploiting your authorization logic and the other runs a scanner and reformats the output. This guide lists established penetration testing companies factually, then gives you the questions that separate the two kinds.
We list ioSENTRIX among the providers because we are one. Every description, ours included, is limited to what the company's own site says. Nothing here is ranked.
A penetration testing company is a security firm that is authorized by a client to simulate real attacks against the client's applications, networks, cloud environments or devices, prove which weaknesses can be exploited, and report the findings with evidence and remediation guidance. The best penetration testing companies combine manual testing by experienced people with tooling, follow a documented methodology such as PTES or NIST SP 800-115, and retest fixes rather than just listing findings.
That definition rules out two things often sold under the same name. A vulnerability scan is not a penetration test, because nobody proved anything. A bug bounty program is not one either, because coverage is whatever the crowd chose to look at. Our comparison of vulnerability assessment vs penetration testing covers the first distinction.
The penetration testing companies below are established providers that publish a clear description of their testing services. They are listed alphabetically, not ranked, and each description uses only what the company's own website says as of September 2026. Recent ownership changes, which matter when you check references, are noted.
Bishop Fox describes itself as "the leading authority in offensive security since 2005." Its penetration testing combines automated testing tools with human expertise, and its Cosmos platform is positioned as a continuous offensive security offering.
Coalfire describes itself as a cybersecurity and compliance services company working in FedRAMP, cloud migration, AI risk and penetration testing. Its DivisionHex team delivers the company's offensive, defensive and managed services.
Cobalt offers offensive security services "from human-led to autonomous pentesting" through a PTaaS platform that combines its own vetted testers, a context-aware platform and AI-powered orchestration. Engagements are purchased through a credit model.
HackerOne combines AI with what it calls the largest community of security researchers. Its offerings include H1 Agentic Pentest, described as AI-driven pentesting that scales with your attack surface, and H1 Bounty, its bug bounty program.
ioSENTRIX is a CREST-accredited penetration testing firm, ISO/IEC 27001 certified and SOC 2 Type 2 attested. Its penetration testing covers web and API, mobile, cloud, network, ICS and IoT, embedded devices and AI and ML penetration testing, delivered as scoped engagements or as PTaaS, alongside red teaming and application security services.
Mandiant is part of Google Cloud, and mandiant.com now redirects to cloud.google.com/security/mandiant. Its red team assessments "emulate a real attacker pursuing custom objectives," and its penetration testing ranges from collaborative assessments to testing specific assets and capabilities.
NetSPI positions its service as PTaaS delivered by in-house penetration testers who work as an extension of the client's team, combining expert-led testing with what it calls purpose-built AI capabilities, through the NetSPI Platform.
Rapid7 describes its penetration testing services as assessments that simulate real-world attacks on your people, processes and technology, evaluated from an external perspective, with strategic recommendations.
Sophos acquired Secureworks on February 3, 2025, and secureworks.com now redirects to Sophos. Sophos Advisory Services lists external and internal penetration testing, wireless testing and web application assessments, using a goal-based methodology with remediation validation.
Synack combines AI-powered penetration testing with human researchers on a PTaaS platform: Sara AI Pentesting, the Synack Red Team for human validation, and the Synack Platform for continuous security validation, with a FedRAMP offering.
LevelBlue completed its acquisition of Trustwave on August 19, 2025, and trustwave.com now redirects to LevelBlue. LevelBlue penetration testing is described as an end-to-end solution covering IT, OT and IoT, physical and people-based testing, delivered by the SpiderLabs team; the page states CREST certification for penetration testing and STAR.
Choose a penetration testing company by defining what you need tested and why, shortlisting firms with verifiable accreditation and experience in that test type, comparing sample reports rather than proposals, checking that manual testing and a retest are included, and confirming who will do the work. Price comes last, because a cheap test that finds nothing is the most expensive one you can buy.
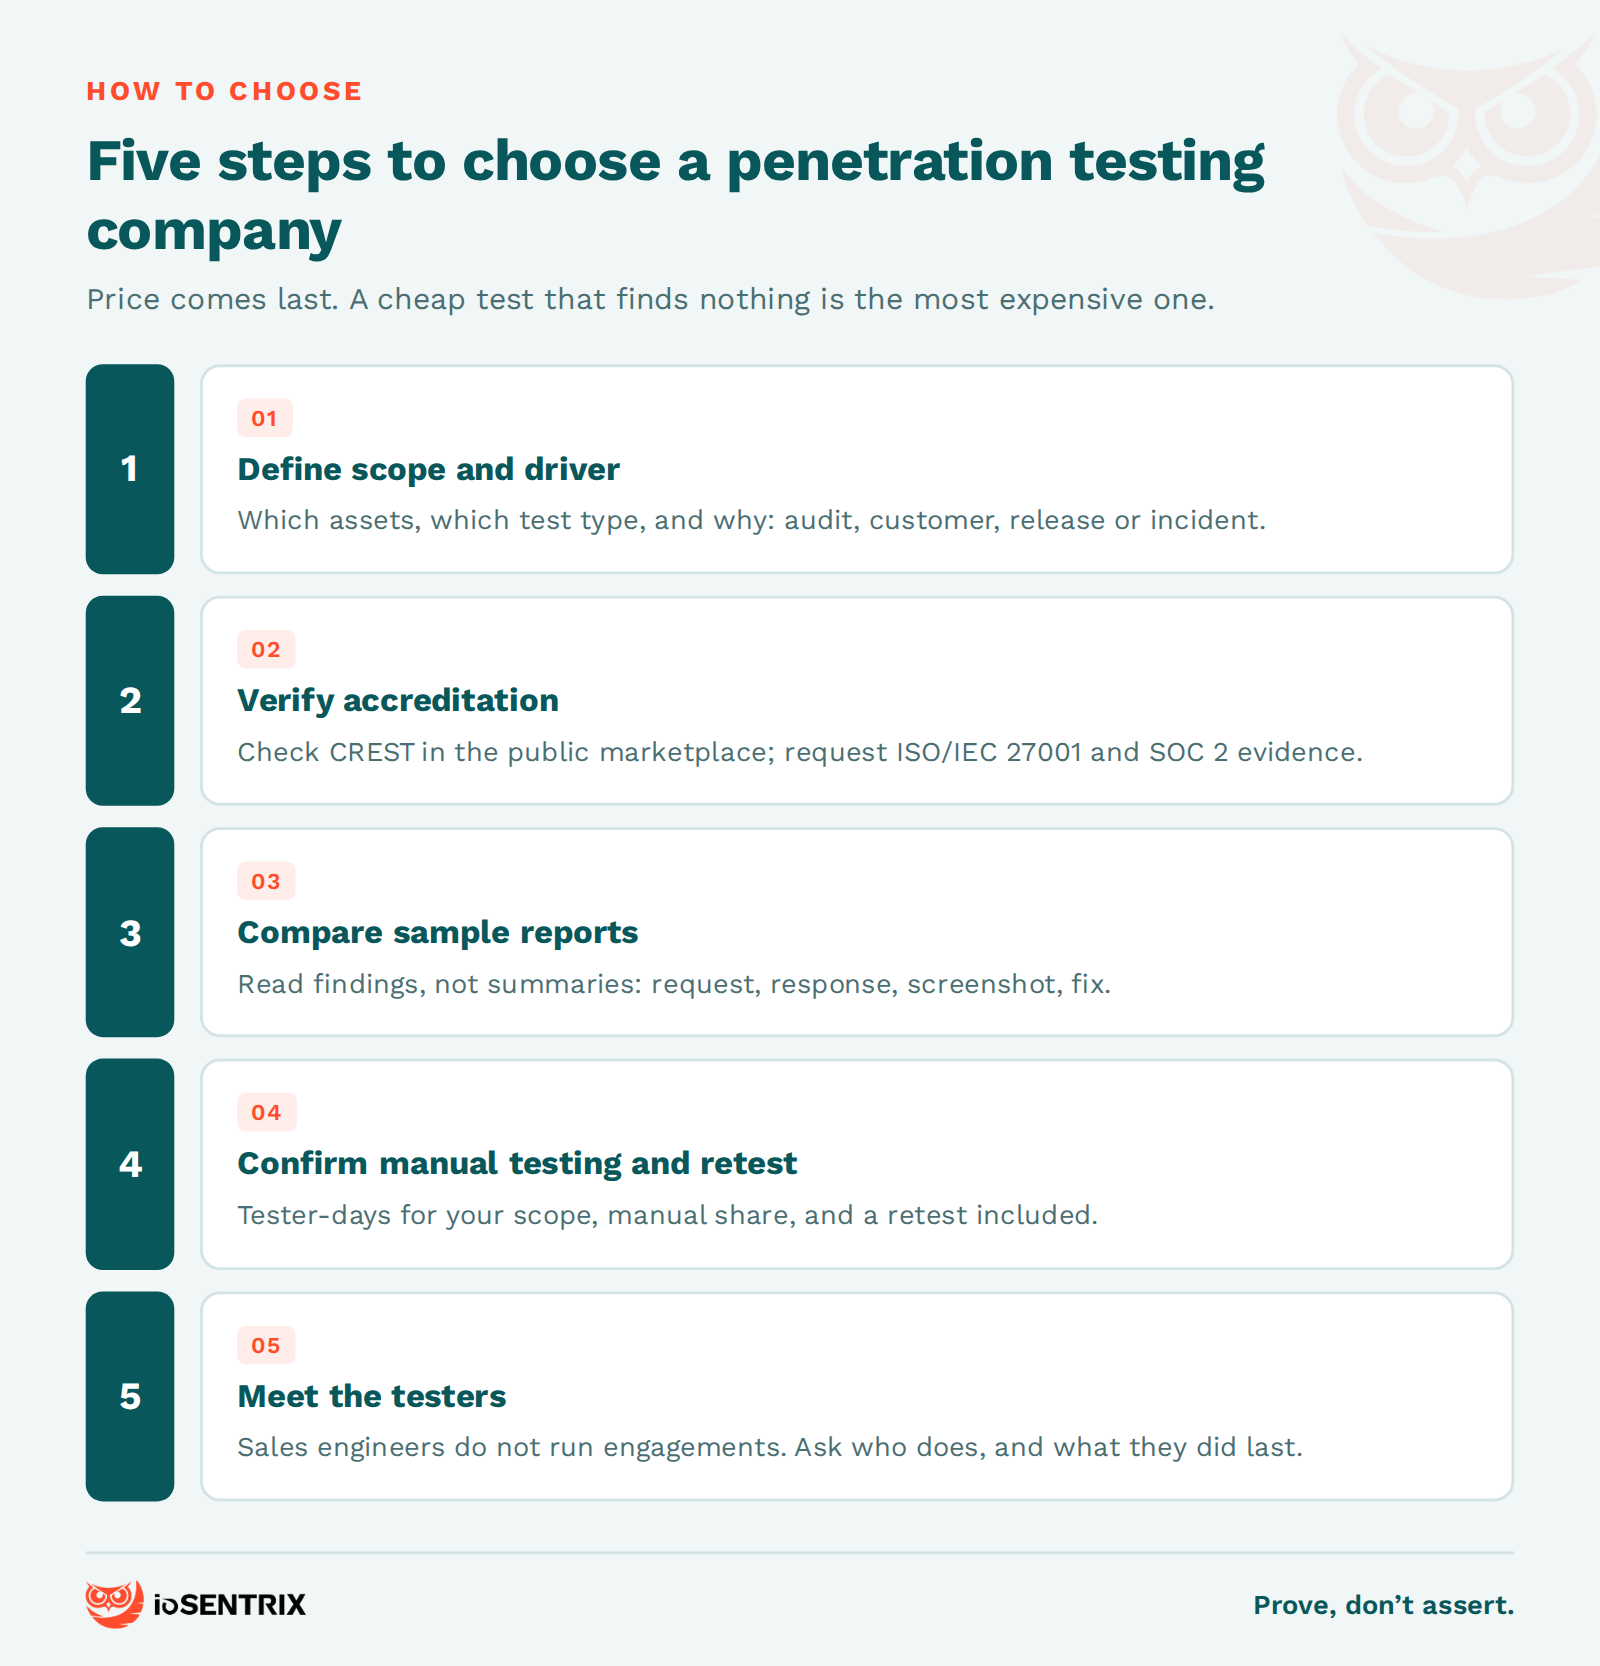
Start with scope. Are you testing a web application, an external network, a cloud account, a mobile app or an AI feature? Is the driver a customer request, a SOC 2 or PCI DSS audit, a new release or an incident? The answers decide which test type you need and which companies fit. Our guide to the stages of penetration testing explains what a full test involves, so you can tell when a proposal leaves stages out.
Then verify rather than trust. CREST accreditation can be checked in the CREST marketplace; ISO/IEC 27001 certificates and SOC 2 reports can be requested. Ask for a redacted sample report from a similar engagement and read the findings, not the executive summary: a real finding has a request, a response, a screenshot and a fix.
Finally, meet the testers. Sales engineers do not run engagements. Ask who will be on your test, what their recent work looked like and how many days they have for your scope. When the day count is too low, the manual testing is what gets cut.
Ask a penetration testing provider questions that force specifics: who tests, how, against what standard, with what evidence, and what happens after the report. The ten below cover most of what goes wrong.
A provider worth hiring will welcome these. Our guide to rules of engagement in penetration testing covers what the seventh should surface.
Penetration testing companies differ most by what they test well, so segment your shortlist by test type before you compare anything else. A firm with deep web application experience is not automatically strong on ICS or on LLM integrations.
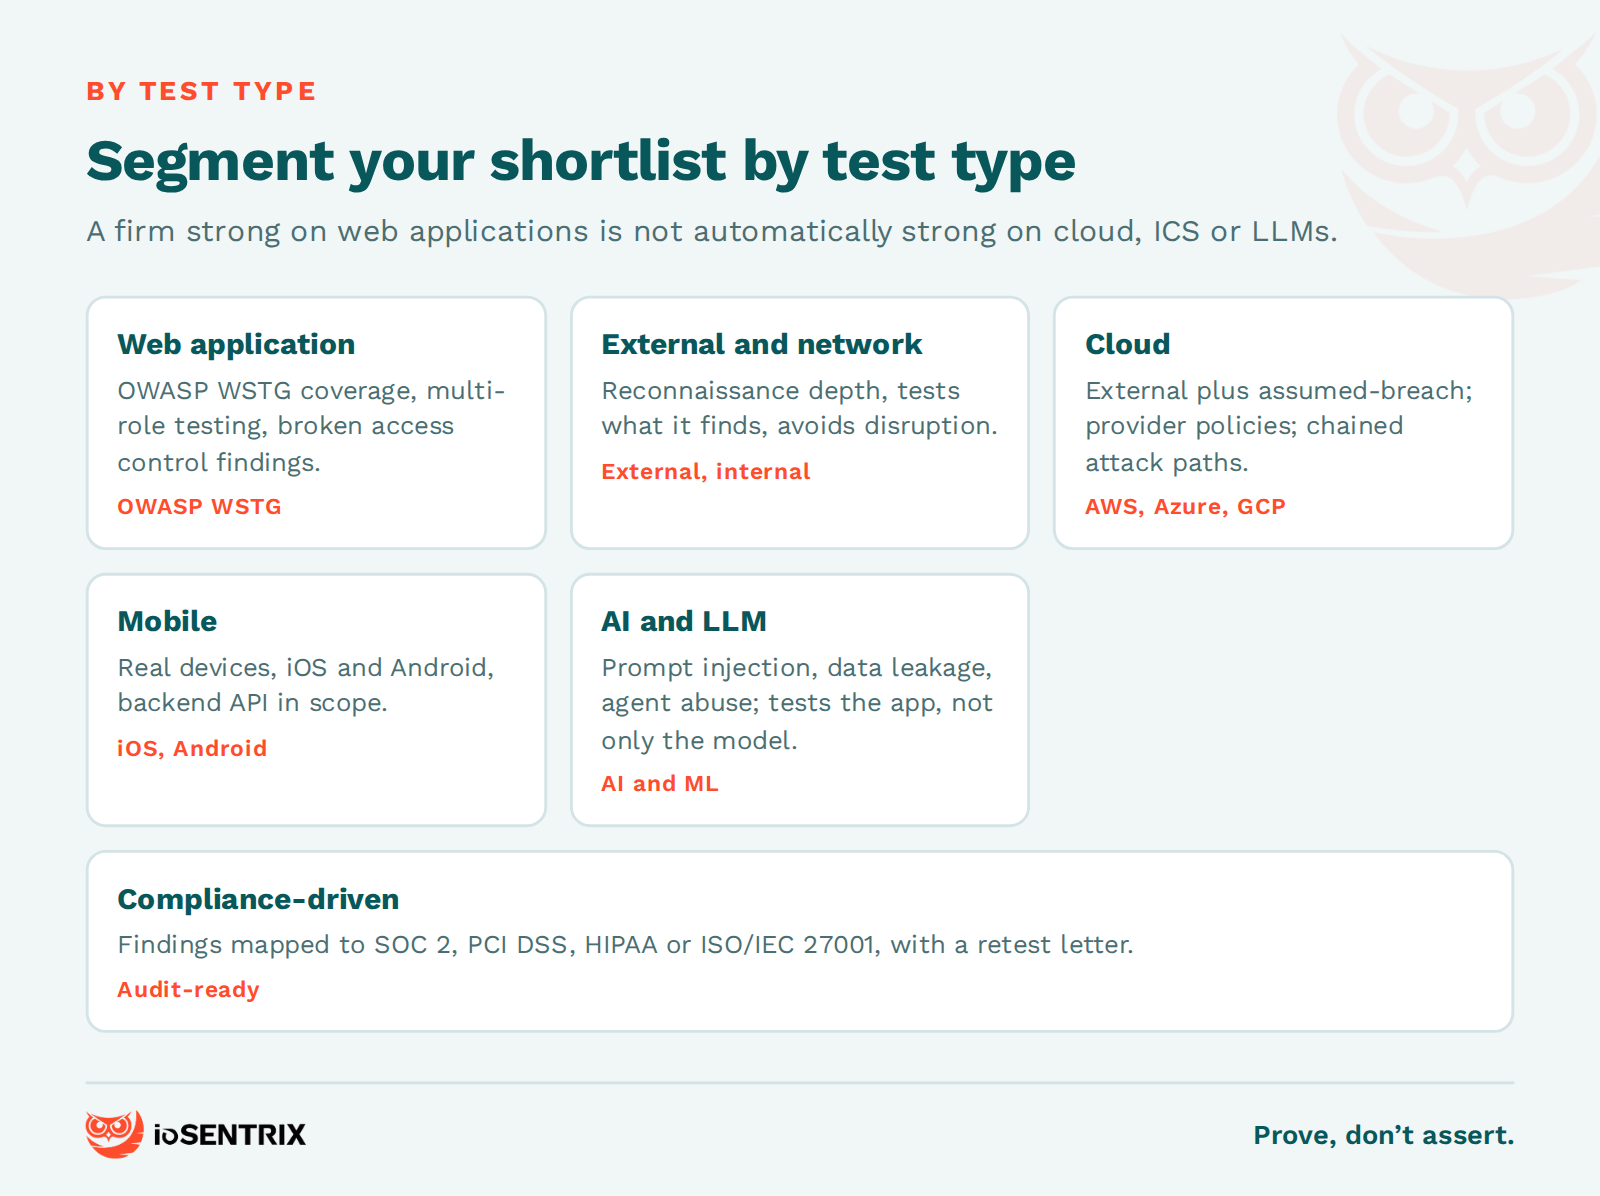
Web application penetration testing companies should test against the OWASP Web Security Testing Guide, cover authenticated and multi-role scenarios, and find the authorization and logic flaws scanners miss. Ask for a sample finding on broken access control. Our guide to web application penetration testing sets the bar.
External penetration testing companies attack your internet-facing footprint from outside; internal network testing starts from an assumed foothold. Ask how they handle reconnaissance, whether they test what they find rather than only what you list, and how they avoid disruption. See internal vs external network penetration testing.
Cloud testing is about identity and configuration more than hosts. Ask whether the firm tests from both an external and an assumed-breach position, how it handles AWS, Azure and Google Cloud testing policies, and whether it chains findings into attack paths. See our cloud penetration testing methodology.
Mobile testing covers the app binary, local storage, the API behind the app and platform controls. Ask whether the firm tests on real devices, covers iOS and Android, and includes the backend API in scope.
AI and ML penetration testing is newer, and fewer firms do it well. Ask for the test cases (prompt injection, data leakage, tool and agent abuse, model access controls), how they test the surrounding application and not only the model, and what evidence they produce. Our guide to choosing AI penetration testing services goes deeper.
PTaaS vendors deliver testing through a platform, with findings posted as they are confirmed and testing that can run continuously or on demand. Traditional providers deliver a scoped project with a report at the end. Neither is better in the abstract; the choice depends on how often your attack surface changes and whether your team will act on findings as they land.
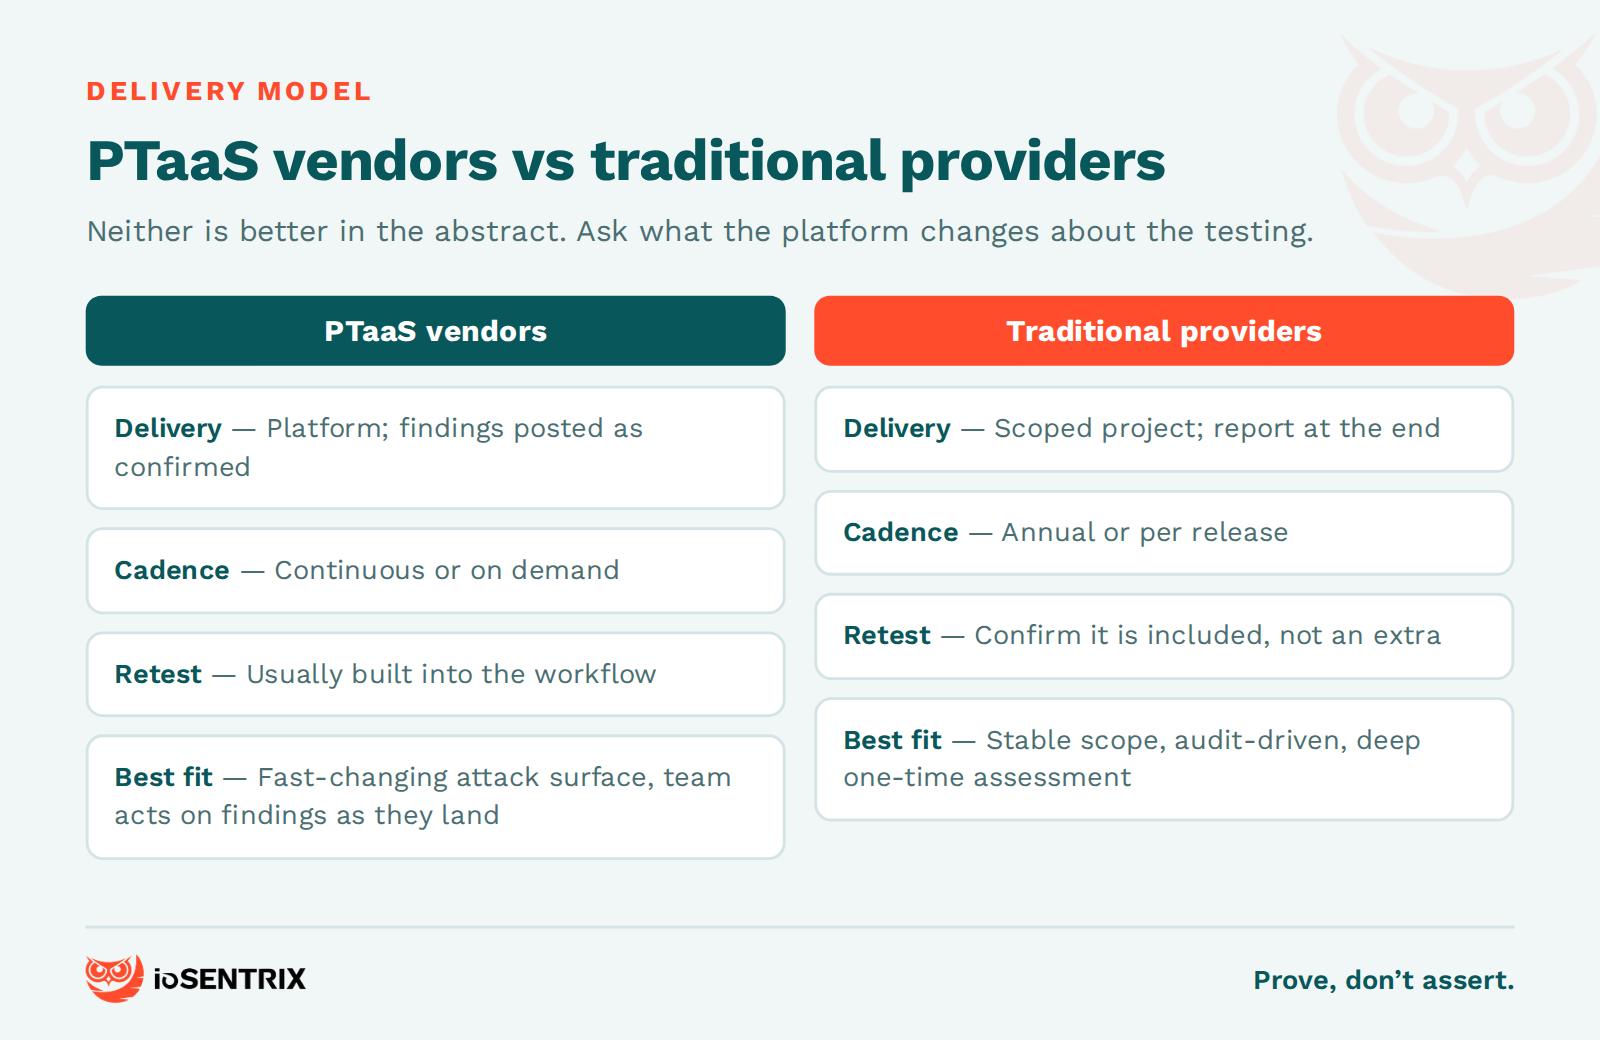
Ask a PTaaS vendor what the platform changes about the testing itself. If the answer is "the same manual testing, delivered faster with retests included," that is a real benefit. If the platform is doing most of the testing, you are buying a scan with a dashboard. Our CISO's guide to evaluating PTaaS platforms covers what to check.
Penetration testing services are priced on tester-days, so cost is driven by scope (how many applications, hosts, roles or accounts), depth of testing, test type, starting access and whether a retest and attestation are included. Two quotes for "a web application test" can differ several times over when one covers two days of scanning and the other two weeks of manual testing across every role. Compare on tester-days and on what is included, and treat a quote with no day count as one you cannot evaluate. Our guide to penetration testing cost and pricing walks through the drivers and typical ranges.
Company-level accreditation matters more than the certifications on a sales deck, because it is the company you are contracting with. CREST accredits penetration testing companies against its standards and lists them publicly; ISO/IEC 27001 certification and a SOC 2 report show that the firm handles your data and findings under an audited control set. Individual tester certifications show that a person passed an exam, which is useful but not sufficient; ask instead what the named testers have done recently on targets like yours. Be precise about what an accreditation covers: CREST company membership is not the same as a CREST-certified individual, and framework alignment is not certification.
Define the test type and driver, shortlist firms with verifiable company-level accreditation and recent experience on that target, compare redacted sample reports rather than proposals, confirm the manual-testing share, tester-days and retest, and meet the people who will do the work. Decide on price only after those are equal.
Ask which frameworks the vendor maps findings to (SOC 2, PCI DSS, HIPAA, ISO/IEC 27001), what the attestation or summary letter looks like, and whether a retest is included, because auditors typically want evidence that findings were fixed. Then apply the same quality checks as any other test; a compliance-driven test that finds nothing real does not reduce risk. Our guide to SOC 2 penetration testing requirements covers one common driver.
PTaaS, penetration testing as a service, delivers penetration testing through a platform where findings appear as they are confirmed and testing can be continuous or on demand. Among the companies listed here, ioSENTRIX, Cobalt, NetSPI and Synack describe PTaaS offerings on their sites, and HackerOne and Bishop Fox describe platform-delivered testing. Ask each what the platform changes about the manual testing itself.
No. CREST accreditation is voluntary, though some customers, regulators and schemes require it. It is a useful signal because it is checked at the company level and listed publicly, but it does not replace reading a sample report and confirming who will test your systems.
ioSENTRIX is a CREST-accredited penetration testing firm, ISO/IEC 27001 certified and SOC 2 Type 2 attested. Our penetration testing covers web and API, mobile, cloud, network, ICS and IoT, embedded devices and AI and ML penetration testing, as scoped engagements or through PTaaS. Every finding is exploited where safe, delivered with evidence and reproduction steps, mapped to the framework you are audited against, and retested after you fix it. We prove what holds rather than assert it.
Put the ten questions above to us. Talk to ioSENTRIX about scoping your next test.